Observed assets
A current view of the devices seen communicating across the monitored network.
THE OTCogniShield PLATFORM
OTCogniShield brings observed equipment, network relationships, security activity, risk decisions and supporting evidence together in one clear interface.
Instead of moving between spreadsheets, specialist network tools and static assessment reports, your team has one place to see what has changed, understand what it means and decide what needs attention.
Illustrative pre-launch platform. Deployment is subject to readiness, agreed scope and an approved passive collection point.
INTERACTIVE PLATFORM PREVIEW
Bring engineering, security, and management together around observed assets, operational risk, and clear next steps.
Where the platform fits: OT, IoT & IIoT architecture · See the topology view →
OTCOGNISHIELD APPLIANCE
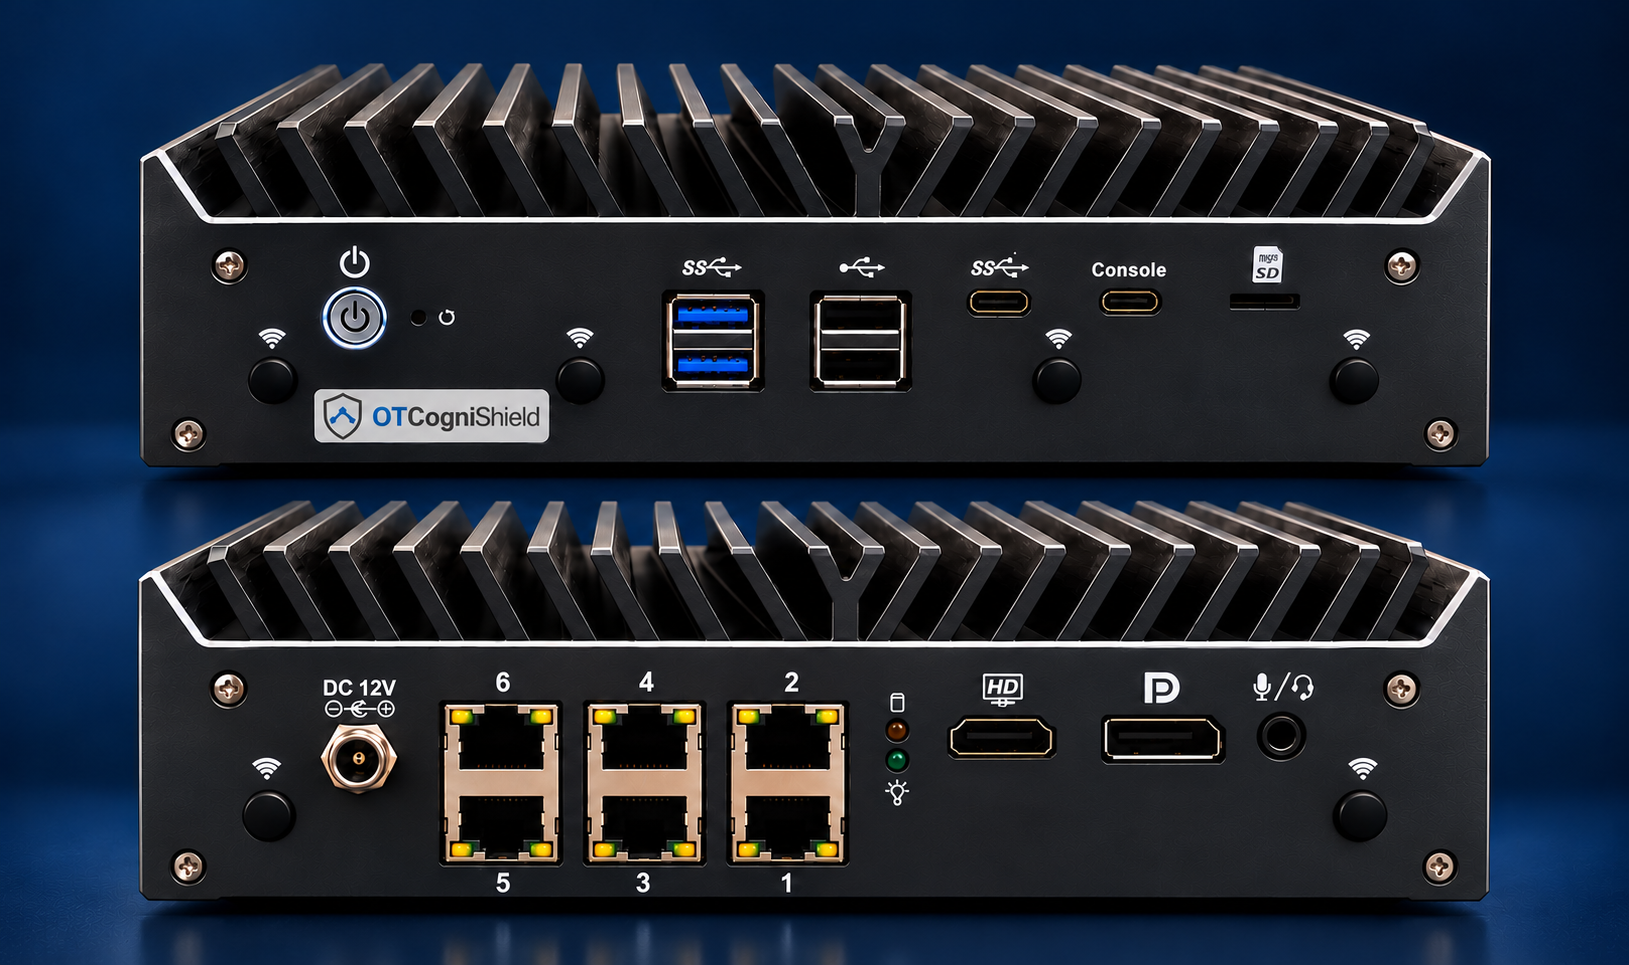
Passive OT, IoT and IIoT visibility from authorised capture data, with offline-capable monitoring and risk intelligence.
Capture points, site coverage and deployment requirements are agreed around your network.
NETWORK & TOPOLOGY
Explore a simplified ICS / SCADA relationship map, with a highlighted review example and clear visibility limits.
Totals from the supplied platform screenshot. Missing links do not establish that an asset is offline.
See the topology view →COMMAND CENTRE
EXAMPLE PRIORITIES
Review access to the production control zone.
Confirm the installed version before planning updates.
Ask the asset owner to validate the observed flow.
OPERATIONAL CONTEXT
Review asset importance, consequences and ownership before deciding what to change.
ASSET DISCOVERY
Bring observed device details, protocols and communication into an inventory your plant team can review.
| Asset | Role | Observed protocol | Assessment scope |
|---|---|---|---|
| PLC — Line 01192.0.2.20 | Process control | Modbus TCP | In scope |
| HMI — Packaging192.0.2.30 | Operator interface | EtherNet/IP | In scope |
| Engineering station192.0.2.40 | Maintenance | OPC UA | In scope |
| Telemetry gateway192.0.2.50 | Sensor aggregation | MQTT | Review required |
Observed details depend on the capture, protocol and available traffic. Your team validates asset identity and scope.
RISK ASSESSMENT
Assess the likelihood and operational consequences, record existing measures, and give the next action a named owner.
Select likelihood and consequence to show a rating.
| Likelihood | 1 Minor | 2 Moderate | 3 Significant | 4 Major |
|---|---|---|---|---|
| 4 Likely | ||||
| 3 Possible | ||||
| 2 Unlikely | ||||
| 1 Rare |
Local assessment bands: Low 1–4 · Medium 5–8 · High 9–12 · Critical 13–16. These are illustrative bands, not an IEC-defined universal scale. Acceptance requires the responsible owner’s decision.
EVIDENCE & REPORTING
OT Security & Risk Intelligence
Assessment evidence
Connect technical findings to scope, consequences, recommendations and evidence. Support conversations with management, auditors and insurers.
Evidence supports review. It does not establish certification or legal compliance by itself.
COMMAND CENTRE
The Command Centre brings the most useful operational and security information to the front.
See newly observed devices, changes waiting for review, open risks, recommended actions and appliance health — without having to interpret raw network traffic first.
A current view of the devices seen communicating across the monitored network.
New or unusual activity worth checking.
Security and operational issues still waiting for a decision or action.
Clear, prioritised next steps for your team.
The technical detail is always there when you need it.
But you should not have to wade through it to understand what needs attention.
ASSET DISCOVERY
OTCogniShield continuously develops an inventory from the factory network traffic it observes.
As equipment communicates, the platform builds a richer picture of PLCs, HMIs, engineering workstations, industrial computers, gateways and other connected devices.
For each observed asset, your team can review and add context such as:
Your engineers remain in control of the record — confirming, correcting and adding operational context as the picture develops.
Passive monitoring can only report on traffic available at the approved collection point.
Quiet devices, isolated networks or information that never crosses that point may not appear immediately.
OTCogniShield makes those visibility boundaries clear rather than pretending the inventory is complete.
EXPLORE ASSET DISCOVERY →NETWORK TOPOLOGY
A list of devices only tells part of the story.
OTCogniShield maps the communications it observes, giving your team a visual view of how equipment, systems and network areas relate to one another.
Move from the whole site down into:
Sites → Network zones → Subnets → Individual assets → Communication paths
Instead of asking:
“What is 10.20.14.32?”
your team can start asking:
“Why is this engineering laptop communicating directly with the Line 2 PLC?”
That is where technical network data becomes a useful operational security conversation.
EXPLORE NETWORK TOPOLOGY →SECURITY ACTIVITY
Not every unexpected communication is a cyber attack.
And not every newly observed device is a threat.
OTCogniShield surfaces activity that deserves a closer look and gives your team the context they need to decide what it means.
The platform recommends where attention may be needed.
Your team makes the decision.
OTCogniShield does not automatically block network traffic, isolate controllers or send control commands to production equipment.
RISK ASSESSMENT
Finding a vulnerability or unexpected connection is only useful if you understand what it could mean for the operation.
OTCogniShield brings observed assets and network context into a structured industrial risk workflow aligned to IEC 62443-3-2.
For each risk, record:
Define the realistic threat scenario.
Record the vulnerability, weakness or route that could make it possible.
Assess the potential impact on production, safety, quality or the wider business.
Record the technical, physical and procedural controls already in place.
Assess likelihood and impact.
Assign responsibility and record the agreed action.
Update the assessment as equipment changes, controls improve or operating conditions change.
No rebuilding the same spreadsheet every year.
EXPLORE RISK ASSESSMENT →VULNERABILITY INTELLIGENCE
A global list containing thousands of security vulnerabilities is not an action plan.
OTCogniShield brings relevant vulnerability intelligence alongside the assets you actually observe, using manufacturer, product and version information where that information can be identified.
That gives your team a much more useful set of questions:
Vulnerability intelligence supports the decision.
It does not replace engineering judgement.
EVIDENCE & REPORTING
Industrial cyber security creates questions long after the initial review.
OTCogniShield keeps those answers connected to the work.
Record assessments, attach supporting evidence, track review status and produce clear reports for internal and external assurance.
Support evidence preparation for:
OTCogniShield supports evidence and preparation. Formal certification and legal compliance remain with the relevant external bodies.
EXPLORE COMPLIANCE & EVIDENCE →LOCAL BY DESIGN
OTCogniShield runs locally on an on-site appliance.
Day-to-day monitoring does not depend on continuously sending sensitive production-network data to a public cloud.
The platform can continue building its operational picture without a permanent internet connection.
Network analysis and operational records are processed and stored locally on the appliance.
Monitoring continues without a permanent internet connection.
Software and security updates are introduced through a controlled process designed for offline-first industrial environments.
APPLIANCE HEALTH & RECOVERY
A monitoring appliance is only useful if you know it is working properly.
OTCogniShield provides a clear view of its own operational state and keeps a record of key maintenance and recovery activity.
So your team can see not only what the appliance is monitoring, but whether the appliance itself is ready to do its job.
PROTOCOL-AWARE VISIBILITY
Factory networks do not behave like ordinary office IT.
OTCogniShield is designed to recognise the industrial protocols used by operational equipment and use that information to add context to the communications it observes.
Initial protocol support includes:
Protocol coverage will continue to develop through testing across different industrial environments.
THE OTCogniShield WORKFLOW
Build a picture passively from the network traffic available at the approved collection point.
See observed devices, relationships, changes and relevant security information.
Add operational context and decide what the risk actually means for your plant.
Give the right person a clear, prioritised next step.
Keep the evidence behind the decision and record what happened next.
Not another stream of technical alerts.
A clearer picture of your production network and a practical way to act on what you find.
DEPLOYMENT & INTEGRATION
One-time engagements connect your plant’s architecture, team and evidence requirements to the platform. Platform deployment is currently being prepared through controlled pilots.
PLATFORM DEMONSTRATION
See how OTCogniShield turns complex industrial network traffic into information your team can understand and use.