Explore documented incidents that affected industrial operations. Follow the evidence, understand the consequences and bring the right questions back to your plant.
Selected public casesHistorical collection · 2015–2024Sources reviewed 11 October 2026
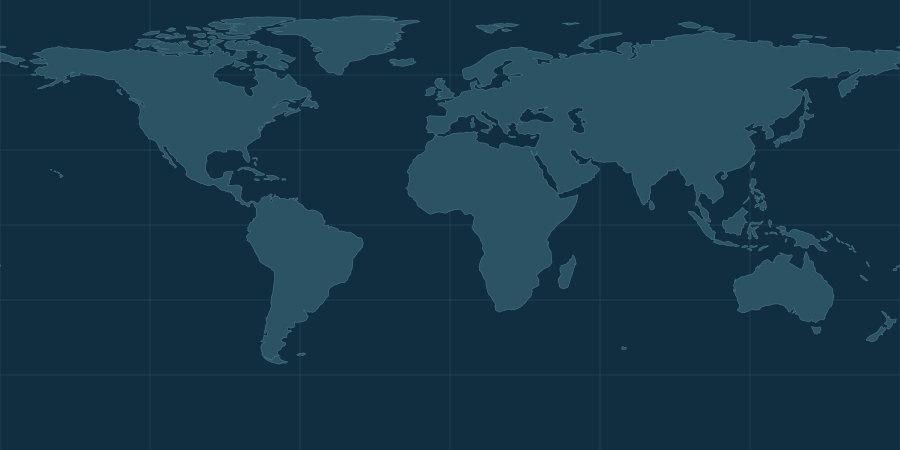
This is a curated educational map, not a live attack feed or a measure of global attack frequency. Markers identify an affected country or a company’s headquarters country, not an exact facility or attacker location.
6 selected public cases · 4 mapped locations. Counts describe this collection only.
Where operations were affectedHistorical cases · select a location
Mapped locationSelected case location
Country-level placement is approximate. Norway represents Hydro’s headquarters; its operations were affected globally. Coastline: Natural Earth.
Control-system activity
FrostyGoop heating disruption
Dragos linked a district-heating disruption to likely use of FrostyGoop. The report describes Modbus commands sent to ENCO controllers, causing incorrect measurements and equipment malfunction.
When and where
January 2024 · Lviv, Ukraine — country-level marker
Reported impact
More than 600 apartment buildings were supplied by the affected utility. Heating was disrupted and remediation took almost two days.
Attribution in the source
No named actor is attributed here. Dragos assessed FrostyGoop was likely used; the entry route was not conclusively established.
Question for your team
Who can reach your controllers, and would your team recognise an unexpected source of Modbus traffic?
Public case summaries are available below. Enable JavaScript to filter the map and select individual cases.
FrostyGoop heating disruption · January 2024
Dragos linked a district-heating disruption to likely use of FrostyGoop. The report describes Modbus commands sent to ENCO controllers, causing incorrect measurements and equipment malfunction.
Reported impact: More than 600 apartment buildings were supplied by the affected utility. Heating was disrupted and remediation took almost two days.
Attribution: No named actor is attributed here. Dragos assessed FrostyGoop was likely used; the entry route was not conclusively established.
Question for your team: Who can reach your controllers, and would your team recognise an unexpected source of Modbus traffic?
Remote cyber activity disrupted electricity distribution. The Canadian Centre for Cyber Security reports that substations at three regional distribution companies were de-energised.
Reported impact: Approximately 225,000 customers lost electricity.
Attribution: The Canadian Centre for Cyber Security attributes the activity to Russian state-sponsored actors. This is reported attribution, not a mapped launch location.
Question for your team: Can you isolate remote access and continue essential operations if supervisory systems become unavailable?
Investigators identified malware interacting with Triconex safety controllers at an industrial facility. A shutdown exposed the intrusion. Published context identifies a Saudi Arabian facility.
Reported impact: The incident disrupted operations and demonstrated an attempt to interfere with safety-system functions. Potential physical harm is distinct from harm actually reported.
Attribution: US prosecutors alleged involvement by a Russian government-affiliated researcher and co-conspirators. An indictment is an allegation; no physical attack-origin point is shown.
Question for your team: Are safety controllers and their engineering access paths separated from routine business and remote-access networks?
Hydro reported a cyber attack across its global organisation. Extruded Solutions faced the greatest operational challenges, while other divisions used workarounds and manual procedures.
Reported impact: Production disruption, demanding recovery work and financial losses. Hydro rebuilt encrypted computers and servers from backups.
Attribution: No actor or origin is assigned from the company account used here. The marker represents the Norwegian company, not every affected factory.
Question for your team: Have you tested recovery of the business systems that scheduling, production and dispatch depend on?
A ransomware attack prompted Colonial Pipeline to proactively shut down its pipeline system. The US Department of Energy records the shutdown and subsequent restart.
Reported impact: Pipeline operations were halted on 7 May; the company announced restart of the full system on 13 May. This record does not establish direct manipulation of pipeline controllers.
Attribution: No actor origin is assigned from the Department of Energy incident summary used here.
Question for your team: Which IT dependencies could force your plant to stop, even if controllers remain operational?
CISA and partners warned that CyberAv3ngers were compromising internet-exposed Unitronics Vision PLCs using default passwords, including at US water and wastewater facilities.
Reported impact: Confirmed controller compromise. The cited bulletin does not quantify service disruption, so no outage total is shown.
Attribution: CISA and partners describe the actors as Iranian IRGC-affiliated. Attribution does not establish where individual connections originated.
Question for your team: Are controllers reachable from the internet, and have commissioning credentials been changed?
A district-heating incident in Lviv shows how access to industrial controllers can become a disruption to essential services. Dragos assessed that FrostyGoop was likely used. The sequence below is a simplified explanation of its published findings.
600+Apartment buildings supplied by the affected utility
Almost two daysReported remediation period during a heating outage
ModbusIndustrial commands sent to ENCO controllers
Simplified reported sequence · the initial entry route is uncertain. The stages have no implied dwell time and do not reproduce the utility’s network layout.
1. Possible entry through an exposed router
Dragos reports possible entry through an undetermined vulnerability in an externally facing router. The exact vulnerability and route were not established. Start by reviewing exposed access points and the people authorised to use them.
Review internet exposure, remote access and the engineering routes to your controllers. Agree who needs access and how it is controlled.
Put traffic in context
Passive visibility can help establish which devices communicate and which protocols they use. Detection of a specific attack requires validated coverage, rules and operational context.
Plan for the consequence
Identify the process that could be interrupted, the people who can respond and the evidence needed to restore operations safely.
How to read this map and its evidence
Six selected incidents and campaigns are summarised from public government, first-party and investigation reports. The collection is not exhaustive, statistically representative or automatically updated.
Markers show approximate country-level locations. They are not incident coordinates. Hydro is mapped by headquarters country and had global operational effects.
Reported actor attribution is shown in each record, with uncertainty or allegations retained. It is not evidence of a physical launch location. No origin-to-target attack lines are drawn.
Control-system activity and IT incidents affecting operations are distinguished. A shutdown alone does not prove a controller was manipulated.
Operational review questions are OTCogniShield’s interpretation of the lessons, not findings about your factory. The FrostyGoop graphic is an explanatory sequence, not captured traffic or a complete forensic reconstruction.
No live telemetry, third-party map tiles, analytics or new AI requests are used by this map. It makes no claim that OTCogniShield detects these specific attacks.
Collection reviewed: 11 October 2026. Contact info@otcognishield.com to flag a source correction.
Bring the lessons back to your plant.
Discuss your access paths, critical processes and recovery priorities with an ICS/OT practitioner.